Different triggers
Vendor review is usually triggered by a purchase. Third-party risk is triggered by exposure, and continues long after the contract is signed.
One shared evidence base
Both programs read the same documents. When each maintains its own copy of the evidence, assessments diverge and audit becomes difficult.
Frequently asked questions
What is the difference between vendor risk and third-party risk?
Vendor risk focuses on risk from suppliers you pay for goods or services. Third-party risk is broader and includes any external party you rely on, such as partners, resellers, contractors, and affiliates.
What is fourth-party risk?
Fourth-party risk comes from your vendors' own suppliers, such as cloud providers, subprocessors, and model providers. You have no direct contract with them, but a failure on their side can still reach your organization.
Why does the distinction matter?
It determines coverage. Programs scoped only to paid suppliers frequently miss partners, integrations, and subprocessors that hold data or influence critical processes.
How do you build an accurate third-party inventory?
Combine procurement and finance records with security tooling, SSO and integration logs, and business owner attestations, then classify each relationship by data access and business criticality.
Who owns third-party risk management?
Ownership is usually shared: a central risk or security function sets the standard, procurement runs intake, and business owners remain accountable for the relationships they use.
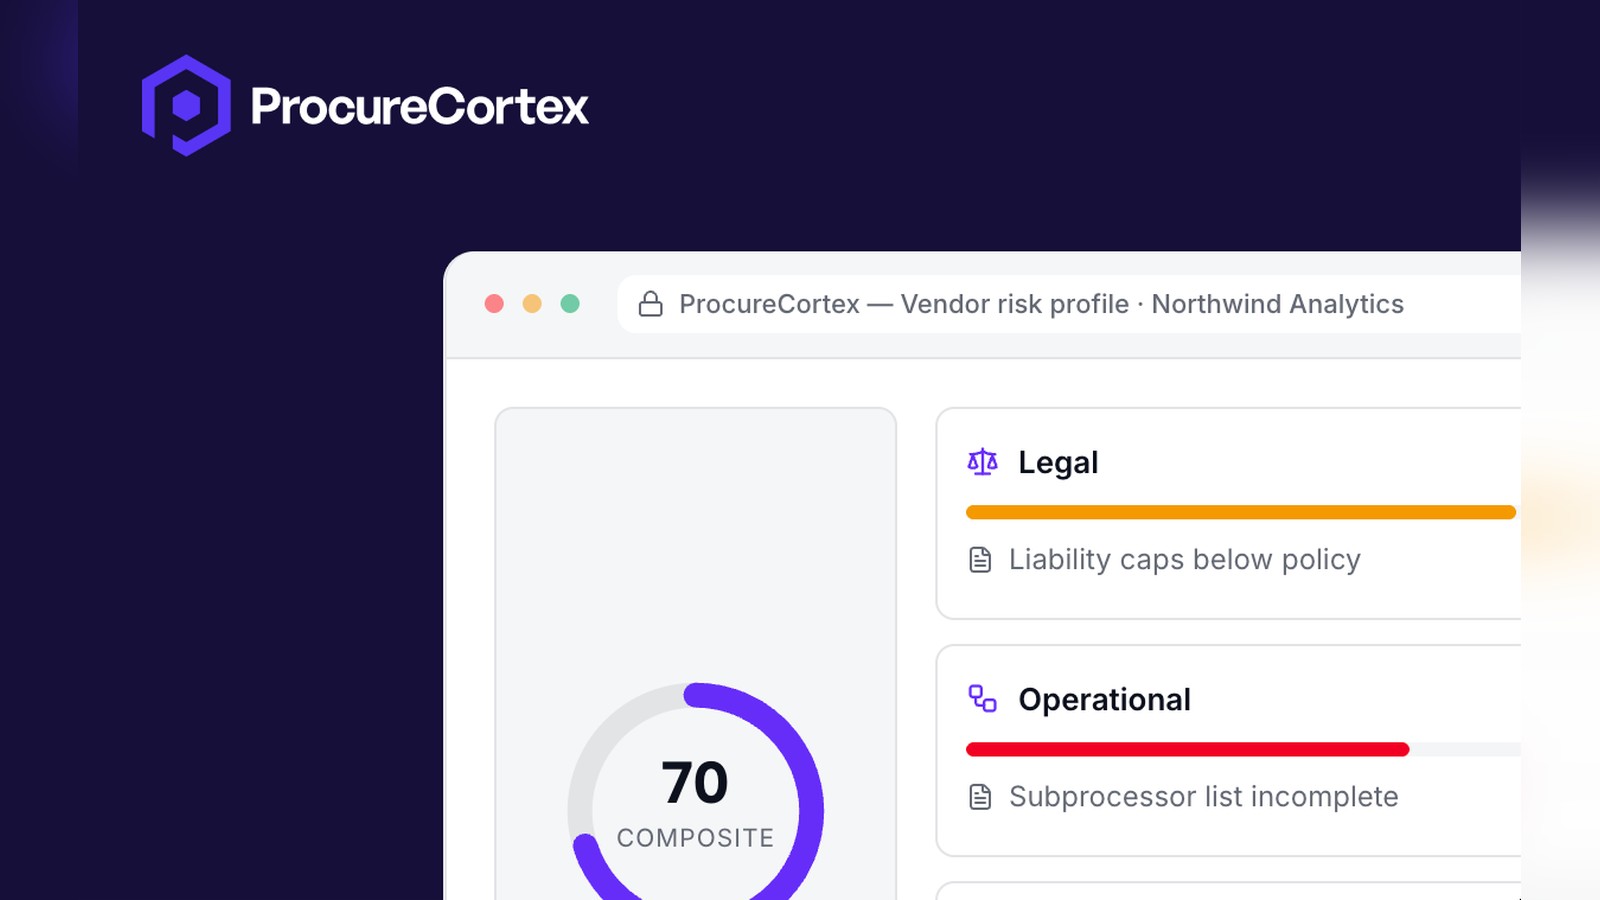
ProcureCortex turns vendor documentation into structured, explainable compliance findings. Explore demo or explore the platform.