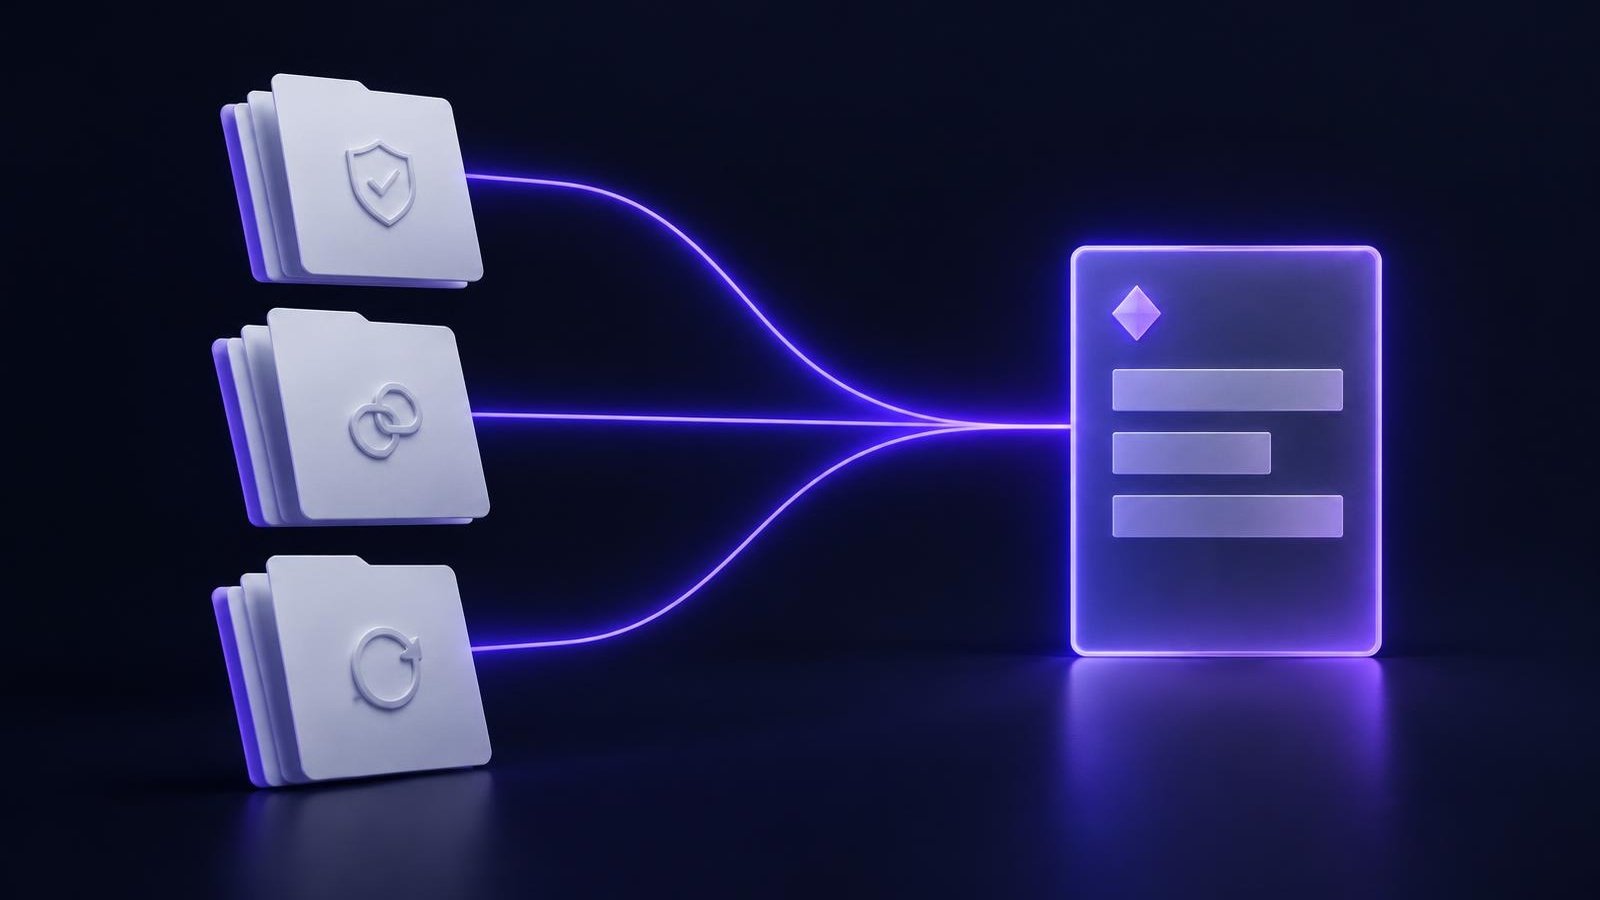
Intake
Capture the vendor, the service, the data involved and the internal owner before any document review begins.
- Vendor profile and business owner
- Data categories processed
- Criticality tier
- Required document set
Evidence collection
Collect the documents that carry commitments, not marketing material.
- SOC 2 report
- ISO 27001 documentation
- Privacy policy and DPA
- Master agreement and annexes
Analysis and review
Compare evidence against the frameworks relevant to the engagement, then review findings by severity rather than reading every page.
Decision and remediation
Record the decision, route validated findings to owners and set a reassessment trigger.
Frequently asked questions
What should a vendor risk assessment checklist include?
It should cover vendor and service scope, data classification, security controls, access management, privacy and data processing terms, compliance certifications, subprocessors, business continuity, incident response, and contractual protections.
Should every vendor complete the same checklist?
No. Scale the checklist to risk. Vendors handling regulated or sensitive data and vendors with system access need deeper review than low-impact tools with no access to customer data.
What is a security questionnaire?
A security questionnaire is a standardized set of control questions sent to a vendor. It is most useful when answers are validated against supporting evidence rather than accepted at face value.
How do you tell a critical vendor from a low-risk one?
Look at data sensitivity, system access, business dependency, regulatory exposure, and the impact of a failure or outage on customers and operations.
Can a vendor risk checklist be automated?
Yes. Evidence extraction, control mapping, gap detection, and prior-version comparison can be automated, while final risk acceptance stays with a human reviewer.
ProcureCortex turns vendor documentation into structured, explainable compliance findings. Explore demo or explore the platform.